Segmentation & boundaries
Test network segmentation and scope boundaries to support assessment evidence.
03 / QSA SUPPORT
TECHNICAL VALIDATION
Discuss assessment requirements and the applicable framework during scoping.
Review the methodologyTest network segmentation and scope boundaries to support assessment evidence.
Use realistic attack conditions to examine whether controls work as intended.
Use risk-ranked findings and mapped controls to inform assessment and compensating-control decisions.
CLEAR ROLE SEPARATION
Exploit Technology provides independent technical validation. It does not conduct audits, issue certifications or attestations, write policies for attestation, or guarantee audit outcomes.
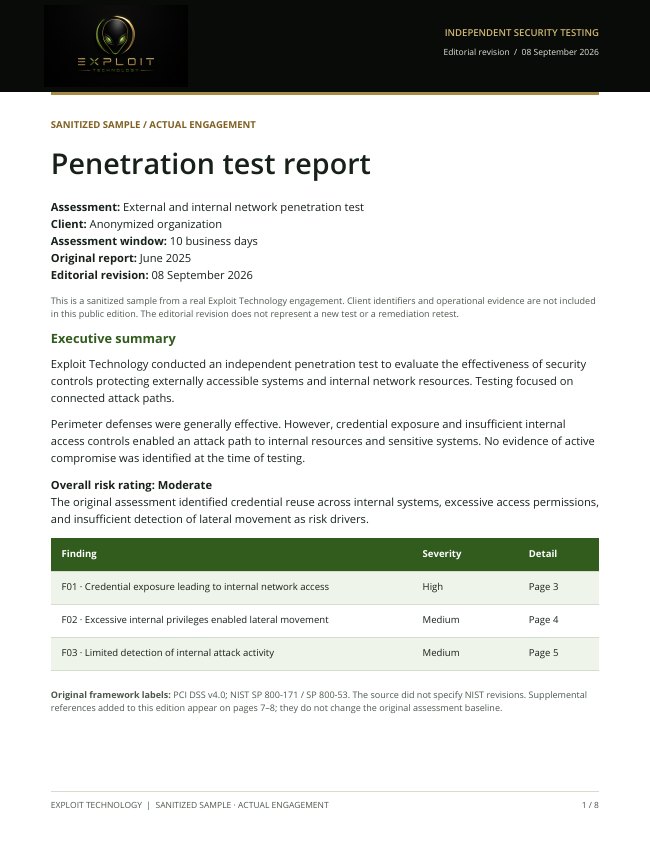
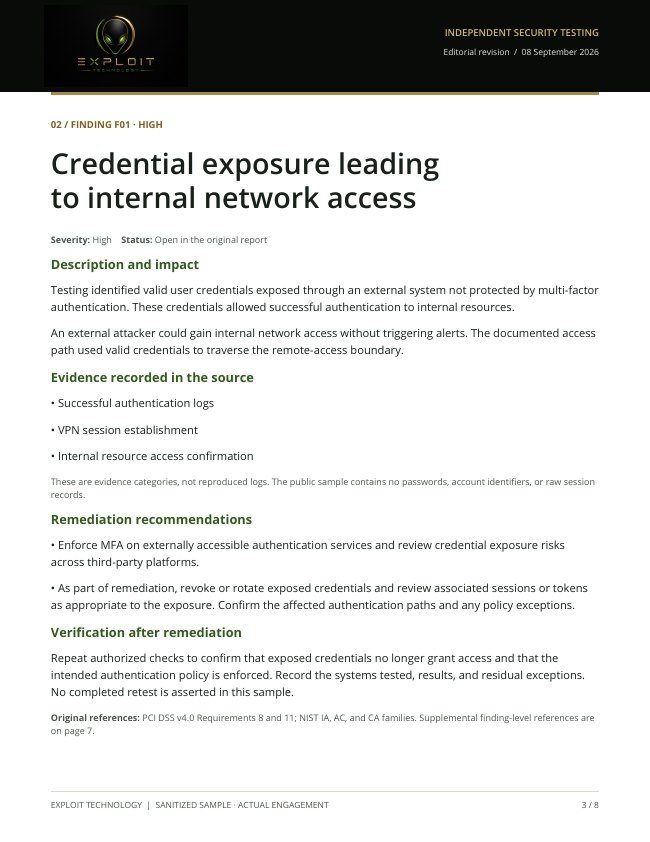
SAMPLE DELIVERABLE
Review a sanitized report from a real engagement, with scope, findings, remediation guidance, and supplemental PCI DSS v4.0.1 and NIST SP 800-53 Rev. 5 references.
Actual June 2025 engagement. Editorially revised in September 2026; supplemental references do not change the original assessment baseline.
Download sample PDF PDF · 8 pages · approximately 2 MBAssessors can also request a methodology and control-mapping overview. Contact Exploit Technology →
LET’S TALK SECURITY
Discuss your environment, assessment needs, and next steps.